
Student data, protected by design
Admissions data is personal: phone numbers of minors, parents’ details, documents and fees. Here is how MizEdu keeps it safe, and how we help your institute meet its obligations under India’s Digital Personal Data Protection Act, 2023.
Each institute sealed off
Every record carries its institute (tenant). Every server query is scoped to the signed-in member’s institute, and the institute is never taken from data a browser sends.
Least privilege
Eight roles with a permission matrix checked on the server for every action. Counsellors see only their own leads; branch staff only their branches.
Audit log
Assignments, exports (with row count), refunds, permission changes, integration changes and settings are recorded with who, what and when.
No card data
Payments go through Razorpay’s hosted checkout. MizEdu never sees, processes or stores card numbers, CVV or expiry dates.
How MizEdu keeps data safe
Encryption in transit
All traffic to the website, app and API uses HTTPS (TLS). Session cookies are HttpOnly, Secure and SameSite, and every change request carries a CSRF token.
Sign-in security
Passwords are stored only as salted hashes. Sign-in with Google or a one-time WhatsApp/SMS code. Login attempts are rate-limited.
Secrets stay on the server
WhatsApp tokens, payment keys and webhook secrets are stored server-side, write-only, and never sent back to a browser.
Backups
Databases are backed up regularly, and access to backups is restricted to authorised personnel.
Signed webhooks
Incoming lead and payment webhooks are verified by signature and de-duplicated, so a replayed event never creates a second lead or payment.
Staff access
Our team accesses customer data only to provide support you ask for, or to keep the service running and secure.
Built for India’s data protection law
For student and parent data in MizEdu, your institute is the Data Fiduciary and BrandMiz acts as your Data Processor, processing data only on your instructions under our Data Processing Addendum.
- Consent records per channel — never assumed from a CSV import
- Opt-out keywords honoured instantly; suppression lists kept
- Retention rules per data type, with anonymisation of closed leads
- Guardian consent document for applicants under 18
- Lead scoring can never use religion, caste, gender, health or income
- Export and correction of a person’s data on request
- A Grievance Officer you can reach directly
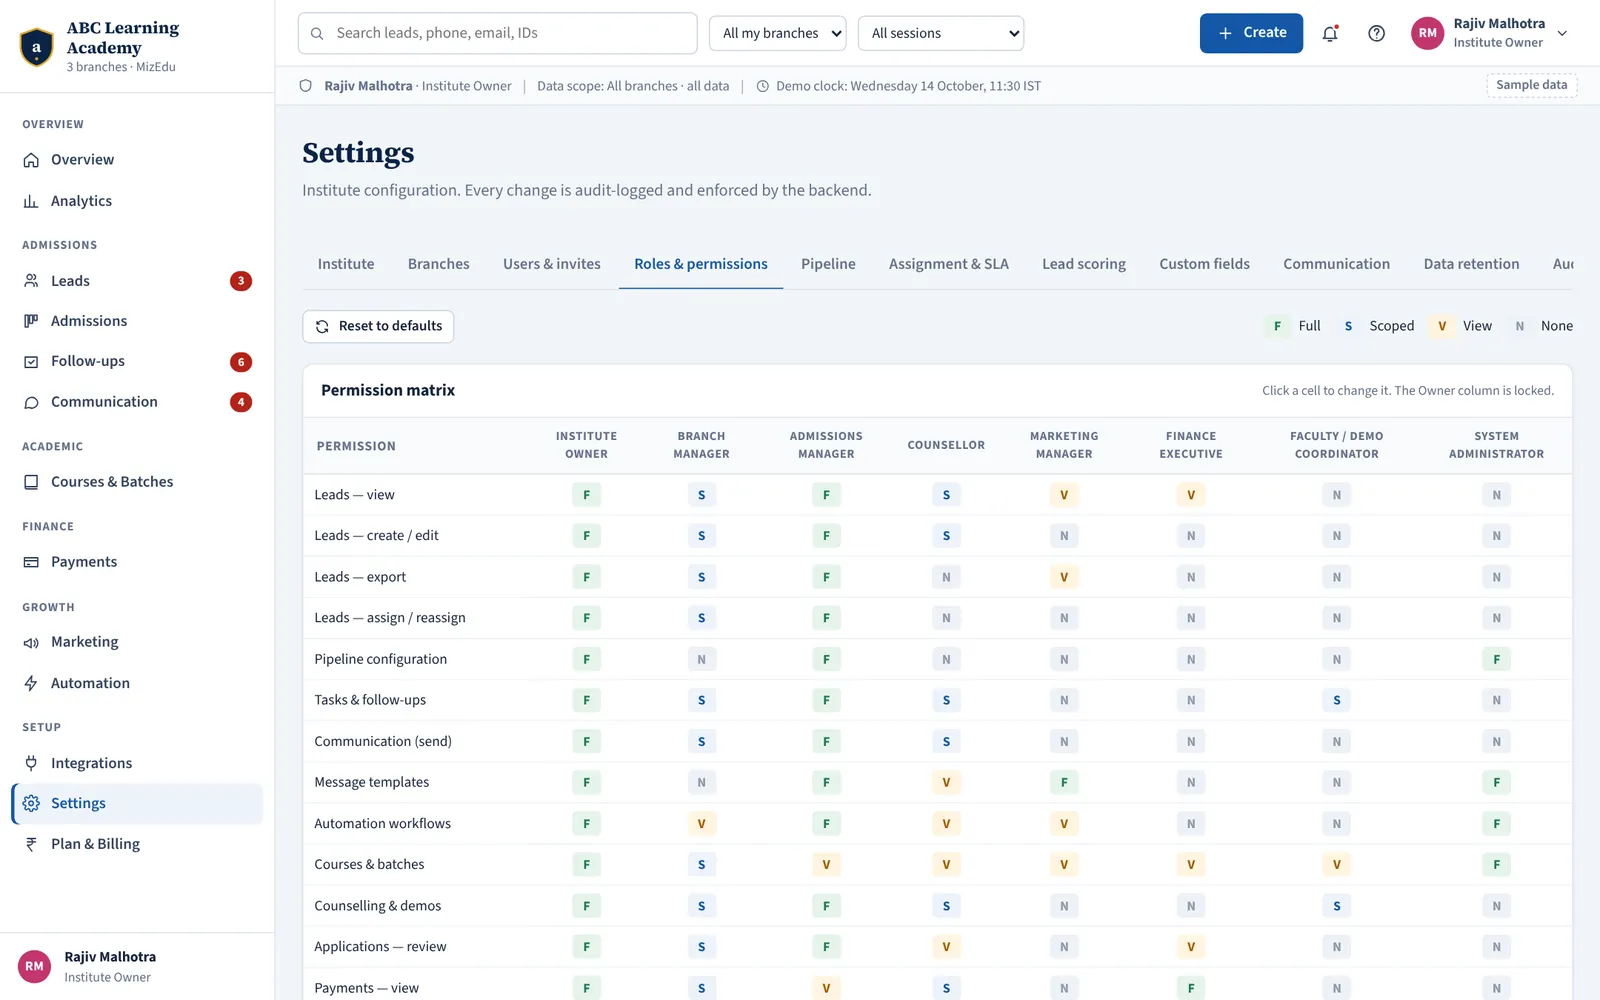
Real MizEdu screen · sample data from the live demo
Keep what you need, for as long as you need it
Institutes can adjust these defaults in Settings → Data retention (Pro plan).
| Data | Kept for | Then |
|---|---|---|
| Lost / closed leads | 24 months after last activity | Contact fields anonymised; aggregate statistics kept |
| Enrolled student CRM records | Enrolment + 36 months | Archived; restricted to Owner and Administrator |
| Message content | 18 months | Message bodies deleted; delivery metadata kept |
| Call recordings (when telephony is connected) | 6 months | Deleted |
| Application documents | Enrolment + 12 months, or 90 days after rejection / withdrawal | Deleted from storage |
| Payment records | As required by tax and accounting law | Retained; card data is never stored |
| Audit logs | 36 months | Immutable, then deleted |
| Opt-out / suppression records | While the institute account is active | Kept so the opt-out is honoured |
Found a vulnerability?
Please write to support@mizup.app with the details and steps to reproduce. Do not access or modify other people’s data, and give us reasonable time to fix the issue before disclosing it. We will acknowledge your report and keep you informed.
Related: Privacy Policy · Data Processing Addendum · Acceptable Use Policy · Grievance Officer
See your admissions desk on MizEdu
Start free — the Free plan is free forever, no card needed — or open the live demo and click through a fully loaded institute as any role.